Jupiter ERP

Trust

Security that fits daily work

Your data stays in your own tenant, transport is encrypted, and operations sit in Germany. Privacy, GoBD, and access control are part of the product from the start.

Hosting in Germany

Built in Hamburg, operated in German data centres.

GDPR and DPA

Data processing agreed at account creation, available in the panel.

GoBD-compliant

Period locking, logs, and a traceable document chain.

Encrypted transport

Panel and API use TLS. Passwords are stored as hashes.

Your own tenant

Each account works in its own data space.

Roles and logs

Rights per module, changes stay traceable.

Privacy, orderly documents, and a clearly separated data space are part of Jupiter ERP. We follow the standards German companies rely on day to day: GDPR, a DPA, GoBD-compliant storage, and the protection themes of ISO/IEC 27001.

Clear roles

You keep responsibility for your customer data. We run the platform for that.

For visits to jupiter-erp.com, Oleart IT Solutions GmbH in Hamburg is the controller. The privacy policy describes what the website processes.

In the application you are usually the controller for data of your customers, suppliers, and employees. We process it as a processor. That split is in the DPA an account admin accepts during setup.

Period locking, permissions, and logs give you the technical base. Procedure documentation and retention periods are something you align with your tax advisor for your own routines.


Privacy

Business data serves your contract, not an ad network.

Jupiter ERP typically holds contacts, document recipients, team accounts, and the content you enter. We do not sell this data, and we do not pass it on for third-party advertising.

On the website we follow data minimisation and purpose limitation. Strictly necessary storage remembers language, appearance and your cookie choice. Reach measurement with Matomo, the referral code, and ad-click measurement only run with your consent. Reach measurement sets no cookies even then. Regardless of that, Cloudflare Web Analytics measures page load times without cookies (details in the privacy policy).

Access, rectification, erasure, and the other data-subject rights for a website visit go through the contact in the privacy policy. Requests from your own customers are yours to answer as controller. We support you within the DPA.

GDPR

Processing under the GDPR and the German BDSG, with measures that fit a cloud ERP.

We follow the principles in Art. 5 GDPR: lawful processing, purpose limitation, data minimisation, accuracy, storage limitation, and integrity and confidentiality. Legal bases follow Art. 6.

Art. 32 calls for technical and organisational measures that match the risk. At Jupiter ERP those are tenant separation, roles, encrypted transport, change logs, and operation in Germany.

If personal data is breached, we inform the controller as the DPA describes: what happened, which data is affected where that is known, and which measures we take. Notifying the supervisory authority stays with you as controller.

  • Tenant separation as the technical boundary
  • Permissions, TLS, and logs as the organisational layer
  • Providers only to run the service, bound by contract
  • Especially sensitive data we agree with you in advance

DPA

The data processing agreement is part of account creation and stays available in the panel.

If you process personal data in Jupiter ERP, you accept a DPA under Art. 28 GDPR when the account is created. Processing is covered from day one.

The binding text is the version an account admin accepts in the panel. Version and time are stored. The same text can be opened again after sign-in.

The contract covers subject matter and duration, nature and purpose, instructions, subprocessors, technical and organisational measures, help with data-subject rights, breach notification, and deletion or return after the contract ends.

Information security

Operations follow the protection themes of ISO/IEC 27001.

ISO/IEC 27001 describes how information security is organised in day-to-day operations: access, cryptography, logging, secure operations, suppliers, and incident handling. We align platform operations with these themes.

In practice that means personal users with roles, encryption in transit, traceable changes, operation in German data centres, and providers bound as subprocessors in the DPA.

For tenders and internal questionnaires we are glad to describe these points in writing, matched to your catalogue.

  • Controlled access through roles
  • Encrypted transport for panel and API
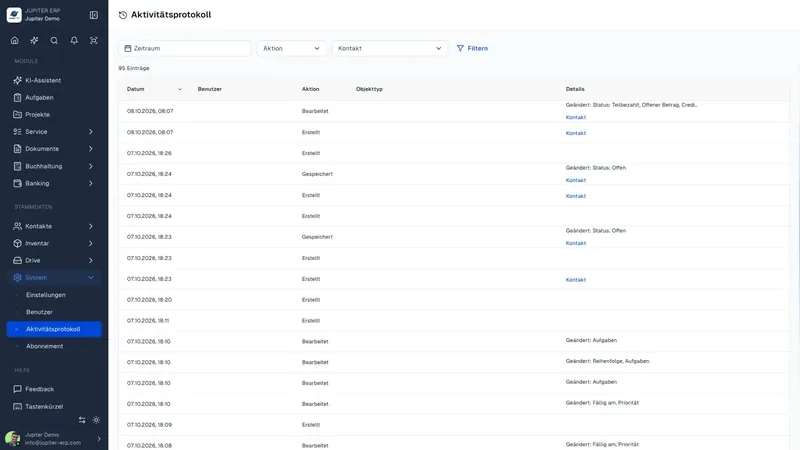
  • Logging of relevant actions
  • Bound providers and a clear reporting path

GoBD

Documents stay traceable, and locked periods stay unchanged.

The GoBD call for traceable, orderly, and unchanged records. Jupiter ERP supports that with PDF storage, clear number ranges, and a document chain from quote through invoice and dunning to credit note.

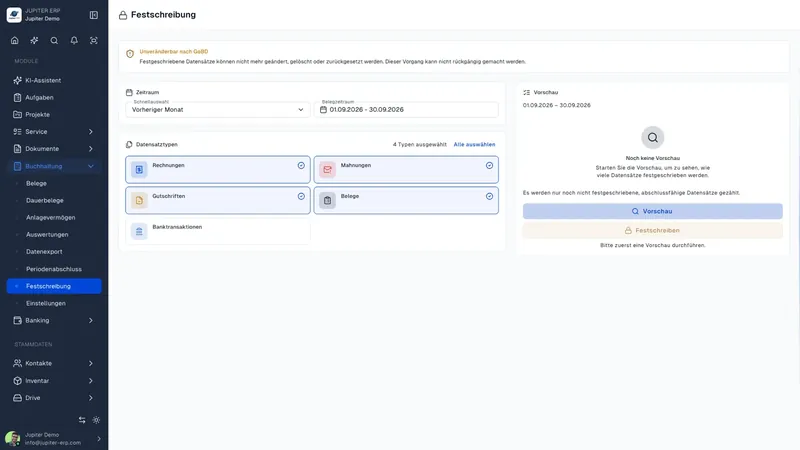
Period locking closes the records you select. After that they can no longer be edited or deleted. You see a preview first, so the period is the one you intend.

Change logs show what the team triggered. For your tax advisor you build a DATEV-compatible export package, from the Business plan, with bank transactions if you want them. E-invoicing in ZUGFeRD 2.x (EN 16931 profile) sits inside the PDF and complements the archive.

  • Period locking for closed periods
  • Logs for internal traceability
  • DATEV-compatible export for your tax advisor
  • ZUGFeRD 2.x inside the invoice PDF

Encryption

Panel, API, and website are served over HTTPS/TLS.

Sign-in data, document contents, and API calls are encrypted on the path between browser, integration, and platform. Your own applications should use the same connection.

We store passwords only as hashes. Account API tokens belong to a user and therefore to exactly one tenant. You can withdraw them when an integration ends.

The platform creates, sends, and exports documents. To do that it processes the contents on the server, protected by tenant separation, permissions, and encrypted transport.

  • TLS for panel, API, and website
  • Passwords stored only as hashes
  • API tokens bound to user and tenant

Tenant separation

Each account has its own data space.

Documents, contacts, files, bank data, and reports stay in the account where they were created. The interface shows only that set.

The same boundary applies to the Account API. An identifier from another account does not return that account's data. Every call runs in the signed-in tenant.

The AI assistant, when you use the AI module, reads only the current account. For larger requirements, dedicated environments and private networking are available on request.

Access and roles

Each team member gets their own role, matched to the job.

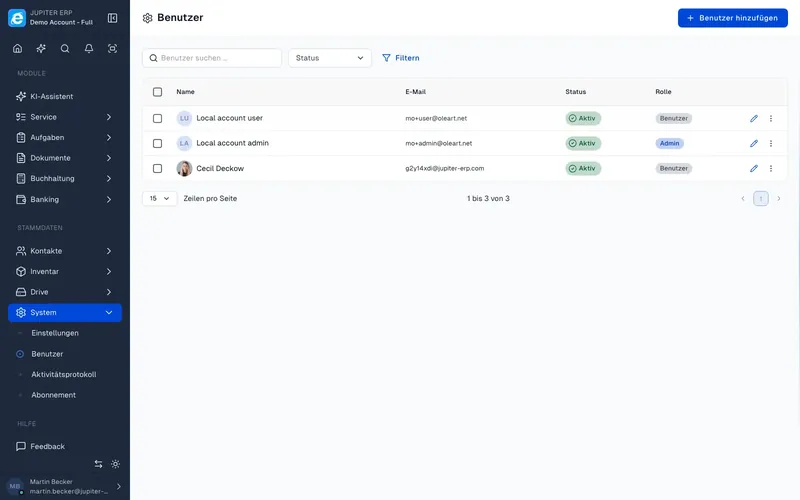
Accounting, service, and administration do not have to share the same rights. You invite people and assign a role, instead of sharing one password.

The customer portal shows a contact only the documents, reports, and files you released for them. Downloads use signed-in links with a permission check.

  • Rights per module and action
  • Invitations with a personal login
  • Portal limited to released content

Logging

Relevant changes stay traceable inside the account.

The activity log records changes to documents, master data, and settings, plus sending and period locking. Who may open the log is controlled by permissions.

You can see internally what the team did, and answer questions from accounting or your tax advisor using the documents and the log.

Hosting and operations

Developed in Hamburg, operated in German data centres.

Jupiter ERP comes from Oleart IT Solutions GmbH. Contract, support, and venue are in Germany. Terms and terms of use are governed by German law.

Backups are part of operations. Hosting, email delivery, and, for the Jupiter AI assistant in the panel, model providers work as operators of the service. Where they process personal data, they are listed in the DPA as subprocessors. The AI provider you use in your own agent over MCP is not a subprocessor of Jupiter ERP.

API and integrations

The Account API is documented and bound to exactly one tenant.

Calls use a personal token. Rate limits and the set of endpoints are in the API reference. Jupiter ERP can connect to a shop, a vertical app, or your own portal while the data space stays closed.

Webhooks and partner integrations, where your plan includes them, report events from your account. You set recipients and secrets yourself. Public forms on this website also use abuse protection.

Retention

Locked documents stay in the account, and export gives you a copy for your own archive.

For books, booking records, and invoices in Germany, retention periods are eight or ten years, depending on the record and when the period starts. Your tax advisor maps the period to the case.

In Jupiter ERP, locked documents stay unchanged while the contract runs. PDF and the DATEV package are the direct way to keep copies for your archive or your advisor. After the contract ends, deletion and return follow the DPA.

Contact

Security and privacy questions reach us directly, and we answer questionnaires in concrete terms.

Reports come in through the contact address. For an existing account, the DPA in the panel is the contractual path between processor and controller.

When procurement, a tax advisor, or a group sends a question list, we go through the points and describe how Jupiter ERP is aligned with the standards they name.

Jupiter ERP

Your first invoice in minutes

Start for free: write invoices on the Free plan. Choose plan, term, and add-ons in the app afterwards. Custom adaptations or API integration? Get in touch.

  • 14-day trial
  • No credit card
  • Hosted in Germany
  • GDPR-compliant
Security and compliance · Jupiter ERP